It's the first time in the history of the world.
When I woke up, the sky was falling!
Today, many OpenCode developers around the world are undergoing "sabotage".
In just a few hours, the token on the account was almost completely illuminated, and the entire AI circuit was completely unstable.
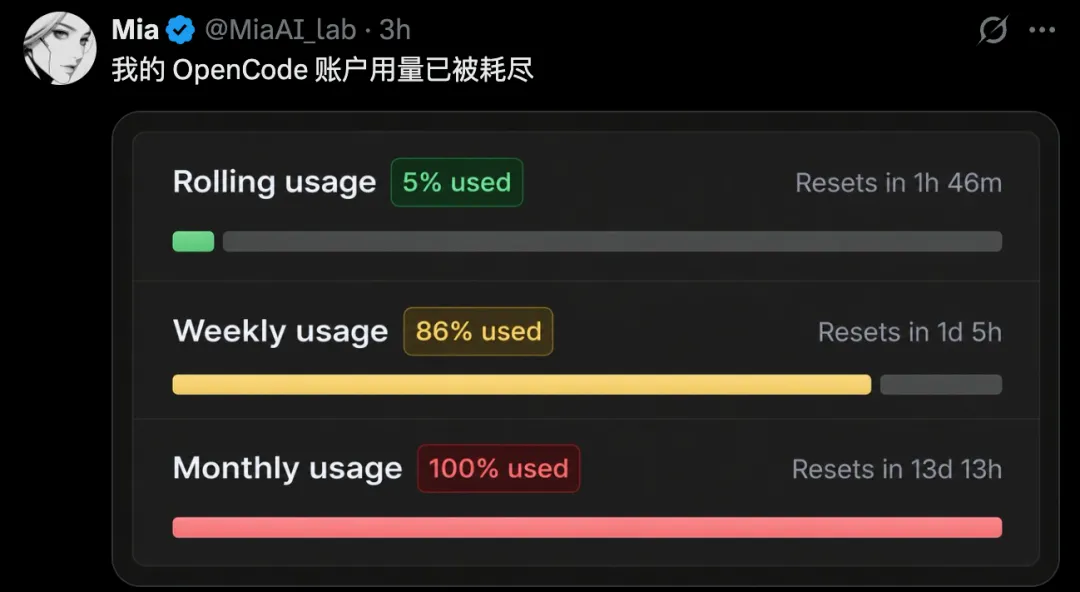
After the incident, the open-source AI programming tool OpenCode was firebased and acknowledged that it was a security breach.
This time around, about 1.4 percent of console users were unfortunate.
They put the OpenAI, Claude, and Gemini API keys in the workspace and they went straight for free.
After the hackers got the Key, it was a fluke to catch the top model.
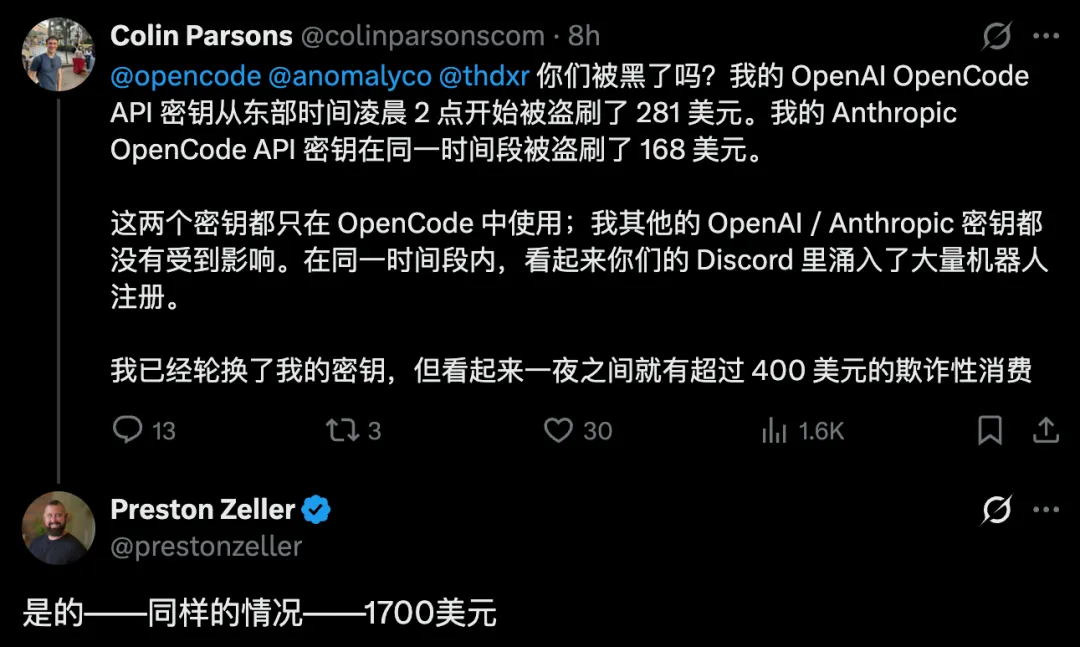
His Anthropic account was wiped out for $400; an older man, more miserable, was directly wiped out for more than 1,700 knives.
OpenCode has been sending developers an alert overnight, calling it a "fire escape" together with Anthropic, OpenAI and Google.
Lydia Hallie, head of Anthropic, responded, "All of the allegedly leaked Claude API keys have now been forcibly deleted".
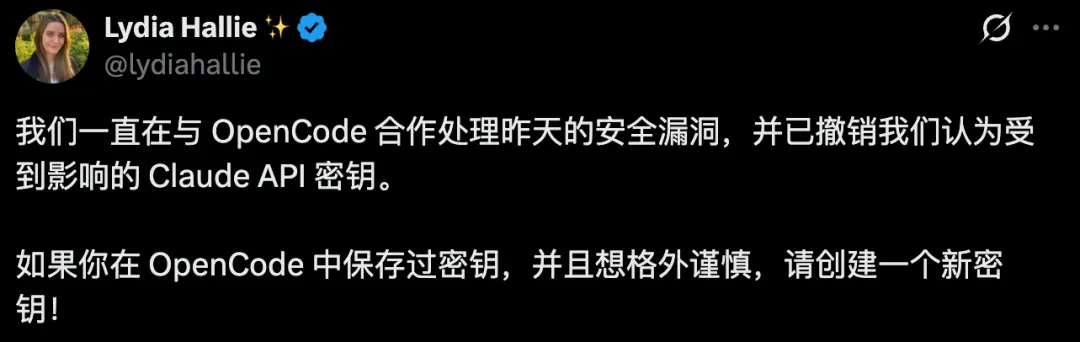 OpenCode breaks a major vulnerability$1,700 stolen in one night
OpenCode was hijacked and exploded very quickly.
In the beginning, it was just a slice where a few programmers were throwing out their own outrageous API bills.
While sleeping, the backstage Token call volume rises vertically as if sitting on a rocket, directly drying the balance to zero, even triggering automatic charging.
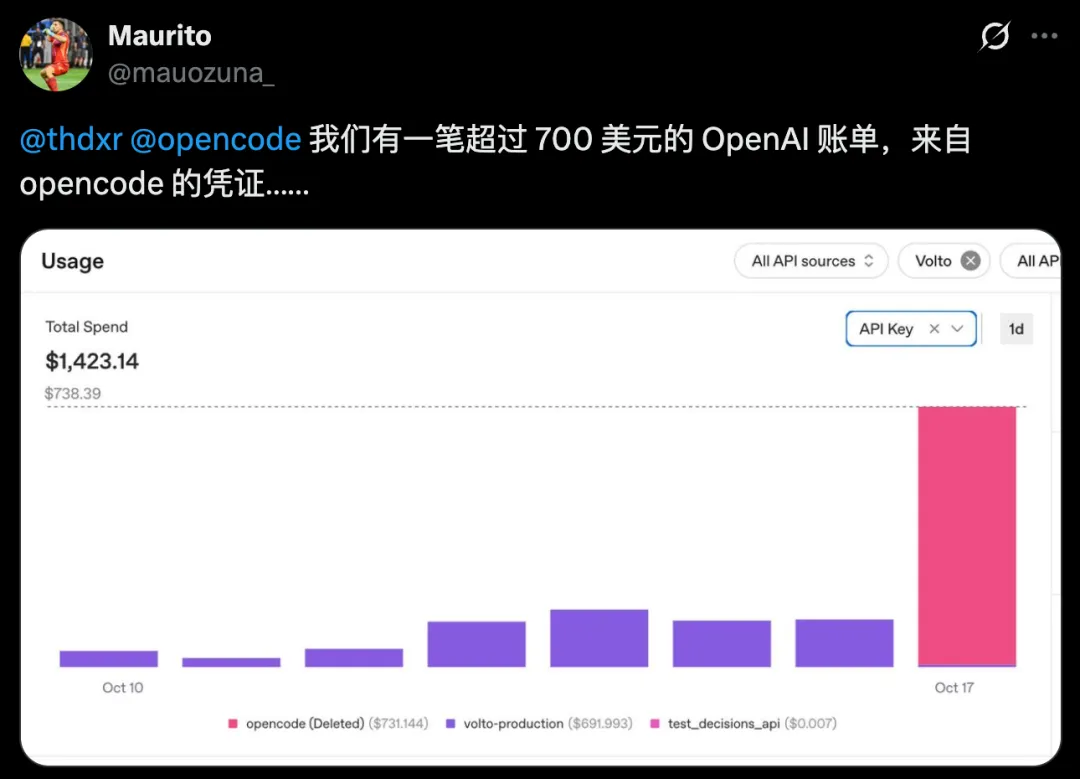
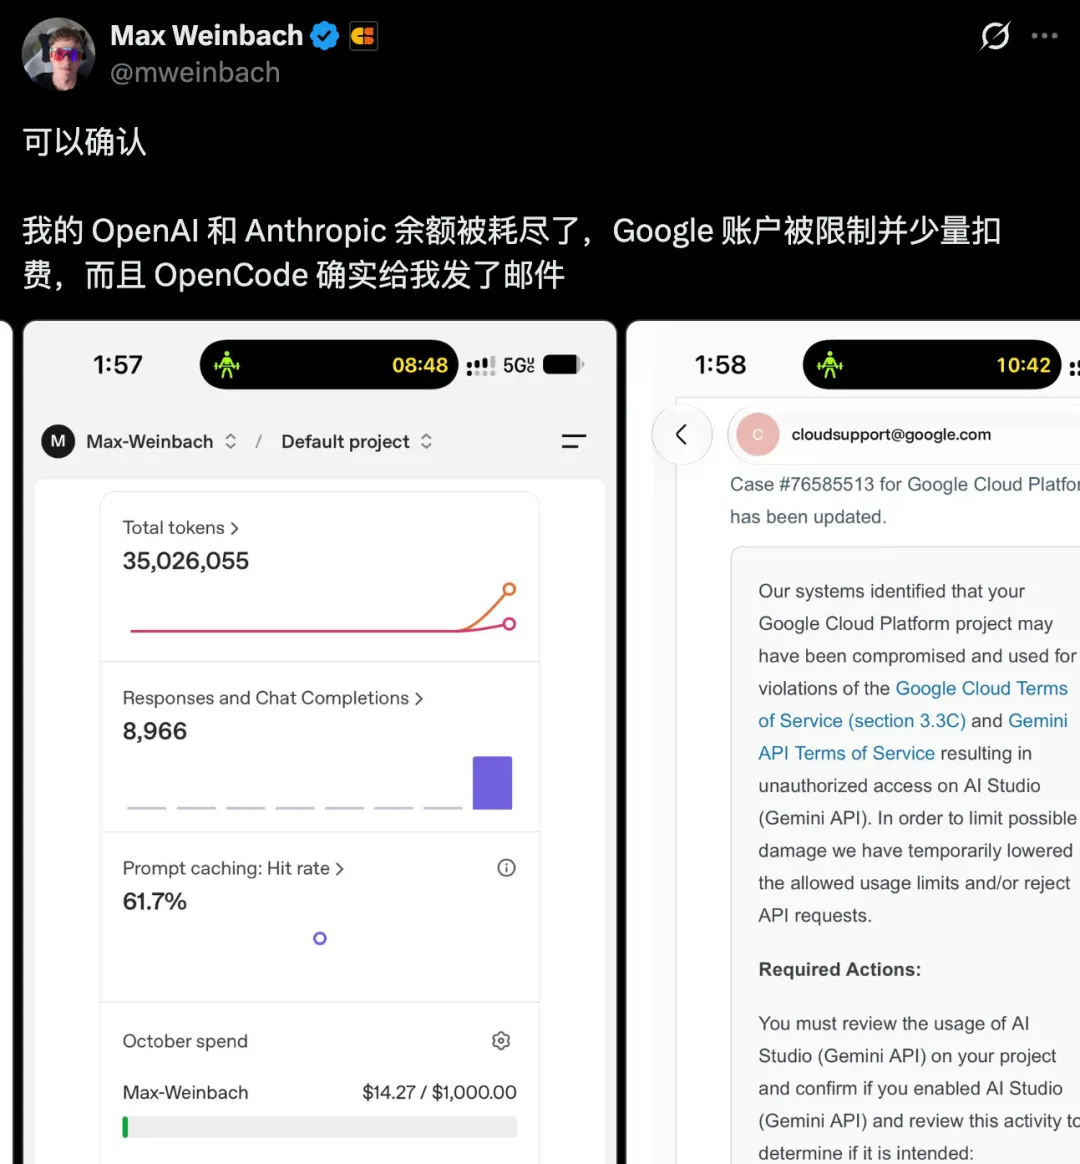
Soon after, someone directly grabbed a screenshot: his own Anthropic account was stolen for $400 without knowing it.
What's even worse is that some people's Google Cloud API bills exploded directly, surprisingly with over $1,000 in price discounts.
The bigger the fire, the more the official OpenCode emergency was launched, reinforcing the speculation that everyone was most worried about.
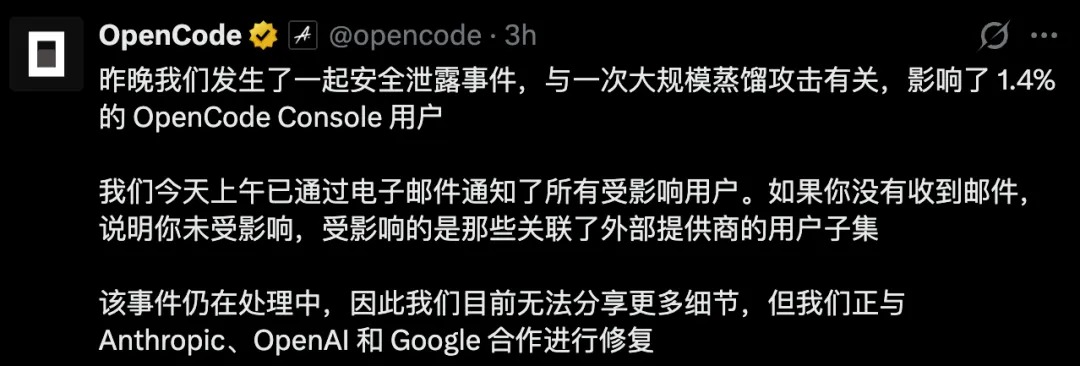
Last night we encountered a security breach related to a massive distillation attack that affected 1.4% of OpenCode Console users.
In an emergency email to users, OpenCode finally gave the bottom line:
This is a "old version of an old system that is preparing to go offline".
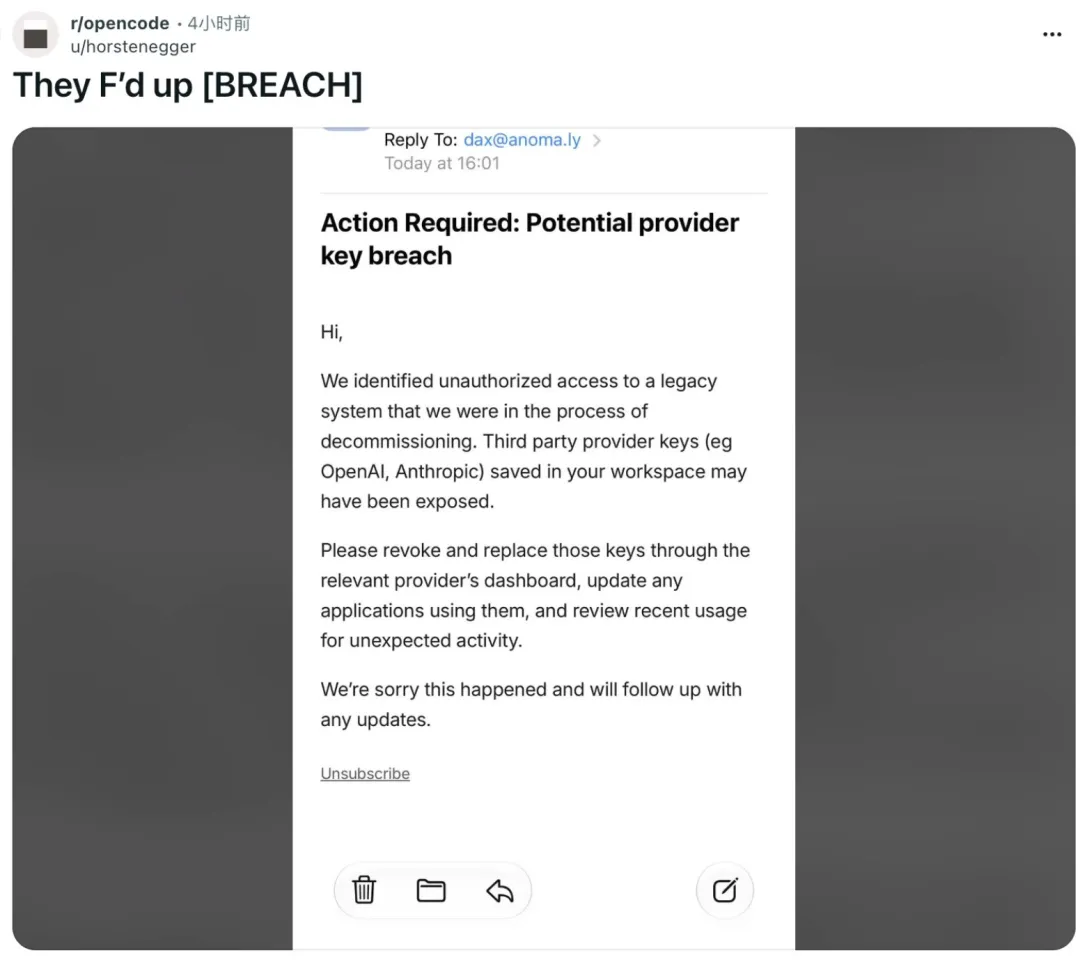 The founder did not escape.
An official search revealed that the system had not yet been shut down and had been directly stolen from the home by hackers.
All third-party server API keys stored in the work area, including OpenAI, Anthropic, etc., may have been exposed.
For now, OpenCode can only urge users to save themselves: immediately cancel and reattach the Keys, update the app settings, and check the most recent call bills carefully.
Ironically, even the founders of OpenCode have not been able to escape this wave of cyber-attacks.
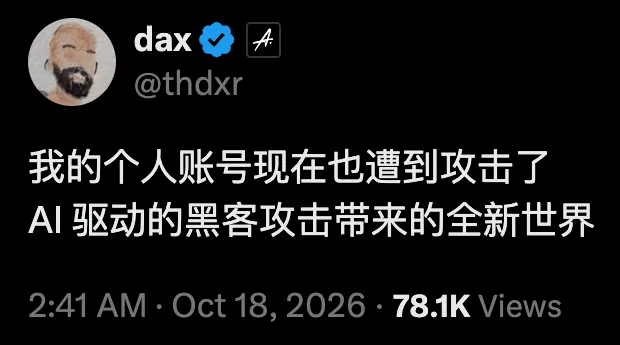
Shortly after the official announcement was released, Dax Raad created a post on X, full of tone and shock:
Now even my own personal accounts are being attacked. This wave of AI automated hacking has opened up a whole new world.
 |  |
What's more dramatic is that hackers steal keys, not to sell them or to steal personal chat records.
They took the Token and went to "train their own model".
In a few hours' window, the hackers who attacked OpenCode converted every penny of these Keys into high-quality tokens of the top models.
To make small models smarter, the core fuel is mass, high-level CoT and code-generating data.
If you go directly to buy OpenAI and Claude's APIs to generate these training data, it could cost you millions or even tens of millions of dollars.
In addition, the major AI giants have long banned out-of-home training of their models in their terms of service, and have deployed extremely strict wind control systems in the background.
So the hackers came up with a very unhelpful trick called knife-killing.Distributed whitewash developers.
By breaking through third-party AI tool pooling platforms such as OpenCode, hackers gained access to hundreds of real developers' API keys at once.
During the entire process, each token consumption is recorded on the victim's developer account.
The AI giant TestingCatalog pointed out that this set a dangerous precedent! This means that using small and medium-sized third-party service providers is becoming unprecedentedly dangerous.
Don't change the password!The old Key is not wasted and the money can burnThe person who received the OpenCode security email, the most important action at the moment, has written in the notification:
To respond to the model server's official controls, revoke and replace potentially leaked API keys.
Changing the login password is not a substitute for revoking the API key.
Just deleting the configuration in OpenCode, or shutting down the operating system, does not automatically disable the already-leaked credentials.
It then checks recent usage and bills, keeps records of unusual calls, consumption times and related notifications, and applies for inquiries and fees to service providers.
Regular applications of old keys also require synchronous updates.
This OpenCode leak was the key of 1.4% of users.
In the AI era, the API key is the developer's second identity card.
Don't hand it over to any "comfortable" console. After all, hackers will never hurt your bills.